 ADAD
Updating your news feed...
NEWS EXPRESS is Nigeria’s leading online newspaper. Published by Africa’s international award-winning journalist, Mr. Isaac Umunna, NEWS EXPRESS is Nigeria’s first truly professional online daily newspaper. It is published from Lagos, Nigeria’s economic and media hub, and has a provision for occasional special print editions. Thanks to our vast network of sources and dedicated team of professional journalists and contributors spread across Nigeria and overseas, NEWS EXPRESS has become synonymous with newsbreaks and exclusive stories from around the world.
Loading banners
Loading banners...
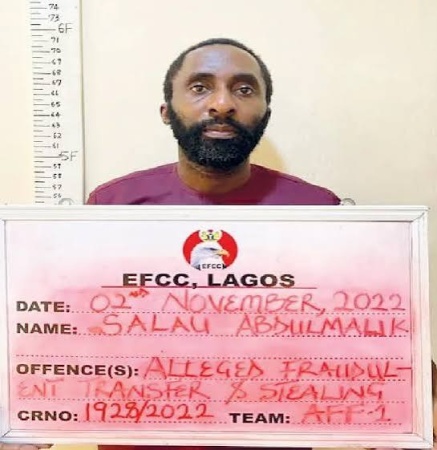
The suspect CREDIT: EFCC
Across the country, cybercriminals, sometimes aided by insiders, exploit vulnerabilities in Nigeria’s banking system to steal billions of naira from unsuspecting customers, VICTOR AYENI writes
Within two days, grief had taken a heavy toll on Mrs Agnes Uwaila (not her real name), making her appear older than her actual age.
The 73-year-old grandmother was known and loved by many in the Ojodu area of Lagos State, where she lived.
It all started a few weeks ago when the septuagenarian visited a leading commercial bank where she held an account.
She had been experiencing difficulties with the bank’s mobile app on her phone and had gone to the bank’s customer care section to resolve the issue.
But on the night of the previous Sunday, she began receiving debit alerts indicating that someone was making withdrawals from her bank account.
Within a couple of hours, Mrs Uwaila made a shocking discovery: about N3m had been withdrawn from her account by an unknown individual.
A friend close to Mrs Uwaila, who pleaded anonymity, told Saturday PUNCH that the woman fainted and was rushed to a hospital, where she received medical attention.
“She worked at the University of Lagos as a non-academic staff member for over 40 years and just retired last year. The N3m stolen from that account by criminals was her entire life savings, as well as the money her daughters sent to her for upkeep.
“She no longer works; she relies on her pension, and someone did this to her. She told us she went to see the customer care representative at the bank, and the man who attended to her obtained her PIN to resolve the problem. That was all.
“We don’t know what really happened. Maybe her PIN was compromised, someone out there had access to it, or the bank app was hacked. They siphoned money from her account. Since the incident, friends and family have been comforting her,” the source said.
One of her neighbours, who gave her name simply as Shola, disclosed that she saw Mrs Uwaila on Wednesday as she struggled to lodge a complaint about the theft.
“I saw her looking so sad while I was on my way to work yesterday morning. She said she was going to UNILAG to change her account number so that the next funds she received would not go into the compromised account and the theft would not recur. It was sad to see an elderly woman in so much grief,” Shola said.
Coincidentally, Shola, who is a businesswoman, disclosed that she had also experienced a similar ordeal after visiting another bank to complain that its mobile app was not opening.
“After some days, someone started withdrawing my money in bits. We eventually had to involve the police, and most of the money was recovered for me,” she added.
Uwaila and Shola’s experiences point to the growing threat of cybercrime and unauthorised access to bank accounts which has raised concerns about the security of Nigeria’s financial institutions.
A massive crypto hack
In June, a multi-stage hacking operation began, triggering a series of security breaches that culminated in what was arguably the largest cryptocurrency theft last Thursday.
Details later emerged of how hackers allegedly used a fake job interview and malicious software embedded in an advertisement to compromise the computers of two Binance software engineers before exploiting a third engineer’s computer to steal $6.3bn worth of cryptocurrency.
Binance said the attack began when an employee on its wallet development team downloaded a tool from the internet that had been tampered with by hackers.
The exchange said it detected the breach afterwards, replaced the affected device and changed the credentials, but the employee’s role and those of other members of the wallet team had been exposed.
Then, in September, a second software engineer seeking a new job downloaded a “malicious code repository” onto their computer after interviewing for what they believed was a legitimate role.
The attack unfolded rapidly on October 29, when 233.46 million XRP, a cryptocurrency, was transferred from five of Binance’s hot wallets, or internet-connected wallets, to an address controlled by the attacker in just four minutes.
The attackers subsequently withdrew other cryptocurrencies, including Bitcoin, the exchange said in its report.
According to Reuters, even as Binance scrambled to secure its systems and freeze withdrawals after detecting the attack late on Thursday, the hackers continued to steal cryptocurrency from the exchange for nearly four hours after the initial theft.
When Saturday PUNCH asked a Nigerian cryptocurrency trader, Michael Efa, whether the recent hack had affected trading activities, he said, “No, it won’t. But we are undoubtedly going to witness a false bull run because of the hack.”
Referring to a cryptocurrency chart for Wednesday, Efa added, “There’s a false buy on this chart, but the market will bleed soonest.”
Areas of similarity
Although bank deposits differ from cryptocurrencies, the cyberattack techniques deployed by hackers in both systems share several similarities.
Cryptocurrency is a form of digital currency that exists electronically and is secured by cryptography rather than issued or controlled by a central bank.
Unlike conventional bank deposits, which are recorded and managed within banks’ centralised computer systems, cryptocurrencies such as Bitcoin and Ethereum are stored and transferred through digital wallets on blockchain networks.
Access to these assets is controlled by cryptographic keys which, if compromised, can enable hackers to transfer funds directly to wallets under their control, often without the involvement of conventional financial institutions.
In conventional banking fraud, stolen funds may be traced through banking records, and transactions can potentially be reversed or disputed through established banking procedures.
However, transactions on most cryptocurrency networks, particularly decentralised ones, are generally irreversible once confirmed.
Cybersecurity experts and government officials have for years warned about hackers using fake job interviews to target employees of companies of interest, noting that such interviews are a well-known hacking technique.
Another method involves phishing and social engineering. Like cryptocurrency hackers, bank fraudsters send fake bank alerts, emails, SMS messages and links designed to trick unsuspecting customers into revealing their PINs, passwords and login credentials, which are then used to steal their funds.
Cybercriminals can also target payment processors, technology vendors, outsourced service providers and other organisations with access to banking infrastructure.
A technology staff member of a commercial bank, who pleaded anonymity, told Saturday PUNCH that hackers could deploy malware to compromise computers and mobile devices.
“These are programmes or codes designed to gain unauthorised access to servers, computers and phones. What these programmes do is harvest data or remotely control a device.
“They can use malware to steal your login details on your bank’s mobile app, disrupt banking transactions and capture your keystrokes. There could also be insider compromises, where a hacker is working within the establishment and has access to financial systems, or where an employee inadvertently downloads a malicious attachment that can aid criminals in breaching the system.
“If a bank’s software has weak authentication, is outdated or contains poorly secured applications, it can be easily breached by hackers. Some hackers can also remotely access computers used by bank employees and, from there, initiate fraudulent transactions,” the technology source said.
Multibillion-naira losses
Figures from the Central Bank of Nigeria’s Payments System Vision 2028 document showed that Nigerian bank customers reportedly lost a cumulative N134.48bn to fraud between 2020 and 2025.
Digital payment fraud and cyber-related losses in Nigeria reached N25.85bn in 2025, representing a 51 per cent decline from N52.26bn in 2024, according to data reported by the Nigeria Inter-Bank Settlement System.
NIBSS noted that the losses peaked at N52.26bn in 2024, driven largely by major incidents, including a single fraud event involving a major entity that was worth about N31.1bn, as well as coordinated cyberattacks involving insiders.
In July 2024, Hope Payment Service Bank lost between N6.5bn and N10bn through cyberattacks and unauthorised transfers, with court charges and prosecution figures citing losses of up to N9.68bn to N10bn.
In October of that year, the Federal High Court in Abuja ordered the freezing of 818 bank accounts across various commercial banks and neobanks, following a request by the Inspector-General of Police to intercept and recover the diverted funds for HPSBank.
Saturday PUNCH gathered that cyber threats have remained a major burden on banks, which have increasingly invested in technology, AI-powered monitoring systems and the CBN’s Bank Verification Number watchlist to detect and intercept fraudulent transactions.
In April 2026, the Nigeria Data Protection Commission launched an investigation into an alleged data breach involving Remita Payment Services Ltd., Sterling Bank and other entities.
Following the incident, the CBN warned the public about cyberattacks aimed at gaining access to Nigerians’ personal accounts.
The apex bank, in a statement signed by its Acting Director of Corporate Communications, Hakama Ali, said hackers were circulating fraudulent messages and emails falsely claiming to originate from the bank.
According to the CBN, misleading messages had been designed to deceive citizens and compromise their personal information.
The regulator said the fake communications, which included emails and online messages, often urged recipients to click on suspicious links while spreading false claims about the bank’s leadership, licensing activities and policy decisions.
“Members of the public are strongly advised to refrain from clicking links or sharing personal information on suspicious websites. Verify the authenticity of all CBN communications through the official website and recognised media outlets.
“Report any suspected fraudulent site, email or message to law enforcement authorities,” the statement read.
Inside bank breaches
Within a period of three years, commercial bank SunTrust Bank Plc was repeatedly targeted in major cyberattacks by suspects who allegedly hacked its computer systems and diverted more than N800m.
On August 6, one of the suspects was identified as 47-year-old Ugochukwu Eze, popularly known as ‘Amazon’, when he was arraigned before the Federal High Court in Lagos.
Eze was arraigned before Justice Friday Ogazi by operatives of the Department of State Services, more than a month after his arrest and detention by the agency.
However, Saturday PUNCH gathered that Justice Ogazi granted Eze bail on September 14.
In January 2025, fraudsters allegedly breached Wema Bank’s computer systems and servers. They reportedly manipulated core financial data, authorisation protocols and internal transfer algorithms to siphon N8.5bn.
In May 2025, the Economic and Financial Crimes Commission arraigned three employees of the bank and four external individuals for their alleged involvement in the manipulation of the bank’s computer data.
Although the defendants pleaded not guilty, a Lagos Special Offences Court sitting in Ikeja convicted and sentenced one of the bank’s employees, Ihechukwu Asiegbu, to three years’ imprisonment in November of that year for unauthorised access to the bank’s computer system to facilitate the theft.
In 2024, TechCabal reported that First Bank had begun legal action to recover about N40bn allegedly diverted by an employee at its head office team in Iganmu, Lagos.
The employee allegedly diverted the funds to 98 bank accounts classified as first beneficiaries, including his wife’s account.
The bank reported the incident to the Nigeria Police Force on March 25, 2024, and obtained three court orders to block hundreds of bank accounts believed to have received the stolen funds.
That same year, the EFCC prosecuted a former Globus Bank ICT employee for allegedly hacking into the bank’s systems and stealing N3.5bn from customers’ accounts using shared employee login credentials.
According to the EFCC’s affidavit, an investigation revealed that “Babatunde Idris Olayiwola, Chinedu Inuma and Igwe George Benedict Obinna hacked into the computer systems of Globus Bank and they transferred the N3.5bn.”
The EFCC was said to have recovered approximately N1.2bn of the stolen funds, although the accused ICT employee denied the allegations, describing them as baseless.
In 2021, a suspect, Femi Salau, was arrested by detectives from the Special Fraud Unit of the Nigeria Police Force for allegedly hacking into the server of the Flex-Cube Universal Banking System to steal N1.87bn.
The police said the suspect was the kingpin of a syndicate that specialised in hacking into the servers of banks and corporate organisations.
Findings by Saturday PUNCH, however, showed that many bank employees at various levels preferred to keep reports of cyber breaches in-house and conceal them from outsiders, including customers.
Under Section 40 of the Nigeria Data Protection Act, organisations that experience a personal data breach likely to result in a risk to the rights and freedoms of individuals are required to notify the NDPC within 72 hours of becoming aware of it.
Where a breach is likely to pose a high risk to affected individuals, organisations are expected to communicate the incident to them immediately, using clear language and outlining steps they can take to mitigate potential harm.
A former senior management staff member of a new-generation bank, who preferred to be identified as Amos Oderinlo, told Saturday PUNCH that theft and losses resulting from cybersecurity breaches could cause banks massive financial losses and reputational damage.
He noted that when customers heard about such incidents, they became jittery, potentially triggering panic withdrawals and further losses.
“When such breaches occur, it’s left for the bank to refund the money, and that is a loss. As to who bears the cost of these losses, it depends. If the loss is the bank’s fault, the bank will bear it, but if it results from a customer’s negligence or carelessness, the customer will bear it.
“We will first have to explain it to the customer, provide evidence of what was compromised and then investigate it. For instance, if a customer was advised to keep their PIN secure, warned against clicking suspicious or unknown links, or told not to answer calls from fraudsters but failed to follow these advisories, ignorance is not an excuse,” Oderinlo said.
How hackers operate
In an interview with Saturday PUNCH, a cybersecurity expert and founder of Web Security Lab, David Odes, explained that attackers could compromise a bank in multiple ways and that a successful attack did not necessarily require them to break through every layer of the bank’s security infrastructure.
He pointed out that attackers sometimes needed to find only one weakness to gain a foothold in a much larger environment.
“That weakness could be an employee who is deliberately targeted because of the level of access or privileges they have within the organisation. It could also be an oversight in the bank’s security processes, such as running vulnerable and unpatched software, something we have seen repeatedly in cybersecurity incidents involving Nigerian organisations.
“On the application side, banking platforms have several potential entry points, particularly their Application Programming Interfaces, which facilitate communication between mobile and web applications, backend infrastructure and other services.
“If these interfaces are not properly secured, attackers may exploit weaknesses in how the bank authenticates users, verifies permissions or processes transactions,” Odes said.
He clarified that, in some instances, the vulnerability was not even in the banking application itself but in one of the services, vendors or third-party organisations connected to it.
“This is an area that deserves particular attention. In one of the high-profile cases I investigated, attackers were able to gain access to an organisation by exploiting a trusted connection with another organisation.
“This demonstrates why institutions cannot limit their security assessments to infrastructure they own and directly manage. They must also understand the security risks introduced by their vendors, partners and other external connections.
“The objective for an attacker is often to establish an initial foothold within the organisation’s network. Once inside, they may spend time understanding the environment, moving laterally, escalating their privileges and identifying systems that give them access to sensitive information or critical banking operations,” Odes added.
Explaining further, the cybersecurity expert said insider threats could make cyberattacks considerably easier. He cited discussions by the EFCC chairman concerning an investigation involving six financial institutions.
In those banks, employees allegedly collaborated with external attackers. The EFCC chairman, Olanipekun Olukoyede, said insiders physically connected devices to banking systems, allowed individuals outside the country to control those systems remotely and facilitated the movement of funds.
“This is a concerning example because it demonstrates that the threat does not always come from someone exploiting a software vulnerability. Sometimes, access is facilitated by someone who already has legitimate access to the institution’s systems.
“Another issue is how organisations manage privileged accounts. Access to critical systems should be restricted to individuals who genuinely require it, and even then, that access should be monitored. An employee’s credentials should not automatically provide unrestricted access across an organisation’s infrastructure,” Odes explained.
According to him, attackers did not always gain access to an organisation and immediately begin stealing money or extracting information.
In many cases, they spent days, sometimes weeks, understanding the environment, identifying valuable systems and determining the extent of their access. That period presented an important opportunity to detect and disrupt their activities before substantial damage was done.
“But if there is one problem large organisations, including banks, must take seriously, it is asset visibility. They usually have hundreds or thousands of assets, and you cannot detect what you cannot see. You cannot effectively investigate activities happening across an environment you do not adequately monitor.
“For instance, banks should continuously monitor authentication activities, privileged account usage, network traffic, API requests and transaction patterns, comparing them against established baselines of normal activity.
“If an employee’s account suddenly begins accessing systems it has never interacted with before, or a banking application starts receiving unusual requests at an abnormal rate, these are indicators that should trigger an investigation. Similarly, unusual transaction patterns, unexpected changes to customer account details and attempts to access sensitive systems outside normal operating hours should not go unnoticed,” Odes said.
Odes further urged banks to deploy security monitoring platforms that collect and correlate activities across their infrastructure and alert security teams to potential threats.
“However, technology alone is not enough. Institutions need properly staffed Security Operations Centres, established incident response procedures and personnel capable of investigating alerts and acting on them. They also need regular penetration testing, vulnerability assessments and independent security audits.
“I would also stress the importance of network segmentation, least-privilege access and Zero Trust security principles. Banks should not operate on the assumption that an individual or device can be trusted simply because it is already connected to their internal network. Even if an attacker compromises one employee’s account or gains access to one system that should not automatically translate into control over critical banking infrastructure. Access should be continuously verified and restricted according to what is genuinely required,” he added.
Why cyberattacks occur – Ethical hacker
Speaking with Saturday PUNCH, an ethical hacker who gave his name only as Khelly explained that human vulnerability was one of the major factors contributing to cyberattacks.
He added that a lack of cybersecurity awareness was another loophole that made major companies vulnerable to hacking and data breaches.
“It could also be due to employee carelessness and curiosity. For example, a bank staff member sees a flash drive outside or inside the company building and, out of curiosity, decides to plug it into a computer to see what is on it.
“That particular curiosity can lead to major damage if the drive contains hidden malware or viruses. Secondly, attacks can come from anywhere, including external and internal threats. External threats come from hackers seeking to obtain certain information, while insider threats originate from within an organisation.
Insider threats mostly arise when an employee feels the company is not treating them as it should. This could stem from resentment, emotional distress or a lack of promotion. Such employees can be extremely dangerous, as they may seek revenge against the company by exposing critical information to attackers,” Khelly explained.
Khelly pointed out that no system was completely immune to hacking, adding that organisations could, however, put measures in place to reduce such risks.
Highlighting these measures, he said organisations needed to “educate their employees about security threats and how they can stay safe. In fact, every employee should undergo security training before being hired, whether as a contract staff member or a permanent employee.
“Another critical measure is ensuring that employees are treated well. This is very important because an angry person can do anything. Make sure everyone gets their basic needs met.
“Another measure is constantly monitoring your systems through a Security Operations Centre team. Organisations should also establish rules and regulations specifically addressing cybersecurity. For instance, no employee should be permitted to use a personal laptop for work.
“Before plugging any flash drive into a computer, it must be checked by the head of security. Employees should not click on suspicious links or open suspicious emails. They should always report suspicious activities to the head of security and the Security Operations Centre team,” Khelly added.
‘Breaches cause financial losses’
Speaking with Saturday PUNCH, a data product manager and AI product strategist, Oladipo Gbolahan, described multibillion-naira thefts resulting from cyber breaches as “an operational crisis and financial loss”.
“Teams shift from building to containment, regulators tighten scrutiny, and new controls often add friction for legitimate customers. The costliest damage is confidence. In payments, trust is the product. Once it breaks, customers limit digital use and financial inclusion slips backwards,” Gbolahan added.
He noted that, having built payments and digital products in Nigeria and Europe, he had observed that most breaches were framed as technology failures, although they were often caused by product and governance failures.
“There is a need to design for compromise. Assume a credential will be stolen, then limit the damage with least-privilege access, transaction limits and real-time AI anomaly detection.
“Every critical dataset also needs a named owner and reviewed access, because what nobody owns, nobody protects. There is also a need to improve customer trust. Make security visible. Alert customers quickly, speak plainly when incidents happen, and give them control over their limits. Security must be a board-level product requirement, not an IT cost,” Gbolahan advised. (Saturday PUNCH)